NSE7_EFW-6.2 Exam Questions - Online Test
NSE7_EFW-6.2 Premium VCE File

150 Lectures, 20 Hours
Your success in Fortinet NSE7_EFW-6.2 is our sole target and we develop all our NSE7_EFW-6.2 braindumps in a way that facilitates the attainment of this target. Not only is our NSE7_EFW-6.2 study material the best you can find, it is also the most detailed and the most updated. NSE7_EFW-6.2 Practice Exams for Fortinet Fortinet Other Exam NSE7_EFW-6.2 are written to the highest standards of technical accuracy.
Also have NSE7_EFW-6.2 free dumps questions for you:
NEW QUESTION 1
View the exhibit, which contains the output of a debug command, and then answer the question below.
Which of the following statements about the exhibit are true? (Choose two.)
- A. In the network onport4, two OSPF routers are down.
- B. Port4 is connected to the OSPF backbone area.
- C. The local FortiGate’s OSPF router ID is 0.0.0.4
- D. The local FortiGate has been elected as the OSPF backup designated router.
Answer: BC
NEW QUESTION 2
What configuration changes can reduce the memory utilization in aFortiGate? (Choose two.)
- A. Reduce the session time to live.
- B. Increase the TCP session timers.
- C. Increase the FortiGuard cache time to live.
- D. Reduce the maximum file size to inspect.
Answer: AD
NEW QUESTION 3
Which of thefollowing statements are correct regarding application layer test commands? (Choose two.)
- A. They are used to filter real-time debugs.
- B. They display real-time application debugs.
- C. Some of them display statistics and configuration information about a feature or process.
- D. Some of them can be used to restart an application.
Answer: CD
Explanation:
Application layer test commands don’t display info in real time, but they do show statistics and configuration info about a feature or process. You canalso use some of these commands to restart a process or execute a change in its operation.
NEW QUESTION 4
An administrator has configured two FortiGate devices for an HA cluster. While testing the HA failover, the administrator noticed that some of the switches in the network continue to send traffic to the former primary unit.The administrator decides to enable the setting link-failed-signal to fix the problem. Which statement is correct regarding this command?
- A. Forces the former primary device to shut down all its non-heartbeat interfaces for one second while the failoveroccurs.
- B. Sends an ARP packet to all connected devices, indicating that the HA virtual MAC address is reachable through a new master after a failover.
- C. Sends a link failed signal to all connected devices.
- D. Disables all the non-heartbeat interfaces inall the HA members for two seconds after a failover.
Answer: A
NEW QUESTION 5
An administrator is running the following sniffer in a FortiGate: diagnose sniffer packet any “host 10.0.2.10” 2
What information is included in the output of the sniffer? (Choose two.)
- A. Ethernet headers.
- B. IP payload.
- C. IPheaders.
- D. Port names.
Answer: BC
Explanation:
https://kb.fortinet.com/kb/documentLink.do?externalID=11186
NEW QUESTION 6
View the exhibit, which contains a partial web filter profile configuration, and then answer the question below.
Which action will FortiGate take ifa user attempts to access www.dropbox.com, which is categorized as File Sharing and Storage?
- A. FortiGate will exempt the connection based on the Web Content Filter configuration.
- B. FortiGate will block the connection based on the URL Filterconfiguration.
- C. FortiGate will allow the connection based on the FortiGuard category based filter configuration.
- D. FortiGate will block the connection as an invalid URL.
Answer: B
Explanation:
fortigate does it in order Static URL -> FortiGuard – > Content -> Advanced (java, cookie removal..)so block it in first step
NEW QUESTION 7
An administrator has decreased all the TCP session timers to optimize theFortiGate memory usage. However, after the changes, one network application started to have problems. During the troubleshooting, the administrator noticed that the FortiGate deletes the sessions after the clients send the SYN packets, and before the arrival of the SYN/ACKs. When the SYN/ACK packets arrive to the FortiGate, the unit has already deleted the respective sessions. Which TCP session timer must be increased to fix this problem?
- A. TCP half open.
- B. TCP half close.
- C. TCP time wait.
- D. TCP session time to live.
Answer: A
Explanation:
http://docs-legacy.fortinet.com/fos40hlp/43prev/wwhelp/wwhimpl/commo
n/html/wwhelp.htm?context=fgt&file=CLI_get_Commands.58.25.html
The tcp-halfopen-timer controls for how long, after a SYN packet, a session without SYN/ACKremains in the table.
The tcp-halfclose-timer controls for how long, after a FIN packet, asession without FIN/ACKremains in the table.
The tcp-timewait-timer controls for how long, after a FIN/ACK packet, a session remains in thetable. A closed session remains in the session table for a few seconds more to allow any out-of-sequence packet.
NEW QUESTION 8
Examine the partial output from two web filter debug commands; then answer the question below:
Based on the above outputs, which is the FortiGuard web filter category for the web site www.fgt99.com?
- A. Finance and banking
- B. General organization.
- C. Business.
- D. Information technology.
Answer: C
NEW QUESTION 9
What conditions are required for two FortiGate devices to form an OSPF adjacency? (Choose three.)
- A. IP addresses are in the same subnet.
- B. Helloand dead intervals match.
- C. OSPF IP MTUs match.
- D. OSPF peer IDs match.
- E. OSPF costs match.
Answer: ABC
Explanation:
https://help.fortinet.com/fos50hlp/54/Content/FortiOS/fortigate-advanced-routing-54/Routing_OSPF/OSPF_Bac
NEW QUESTION 10
Which the following events can trigger the election of a new primary unit in a HA cluster? (Choose two.)
- A. Primary unit stops sending HA heartbeatkeepalives.
- B. The FortiGuard license for the primary unit is updated.
- C. One of the monitored interfaces inthe primary unit is disconnected.
- D. A secondary unit is removed from the HA cluster.
Answer: AB
NEW QUESTION 11
What events are recorded in the crashlogs of a FortiGate device? (Choose two.)
- A. A process crash.
- B. Configuration changes.
- C. Changes in the status of any of the FortiGuard licenses.
- D. System entering to and leaving from the proxy conserve mode.
Answer: AD
Explanation:
diagnose debug crashlog read
275: 2014-08-05 13:03:53 proxy=acceptorservice=imap session fail mode=activated276: 2014-08-05
13:03:53 proxy=acceptor service=ftp session fail mode=activated277: 2014-08-05 13:03:53 proxy=acceptor service=nntp session fail mode=activated278: 2014-08-06 11:05:47 service=kernel conserve=on free=”45034 pages” red=”45874 pages” msg=”Kernel279: 2014-08-06 11:05:47 enters conserve mode”280: 2014-08-06 13:07:16 service=kernel conserve=exit free=”86704 pages” green=”68811 pages”281: 2014-08-06 13:07:16 msg=”Kernel leaves conserve mode”282: 2014-08-06
13:07:16 proxy=imd sysconserve=exited total=1008 free=349 marginenter=201283: 2014-08-06 13:07:16 marginexit=302
NEW QUESTION 12
A FortiGate is configured as an explicit web proxy. Clients using this web proxy are reposting DNS errors when accessing any website. The administrator executes the following debug commands and observes that the n-dns-timeout counter is increasing: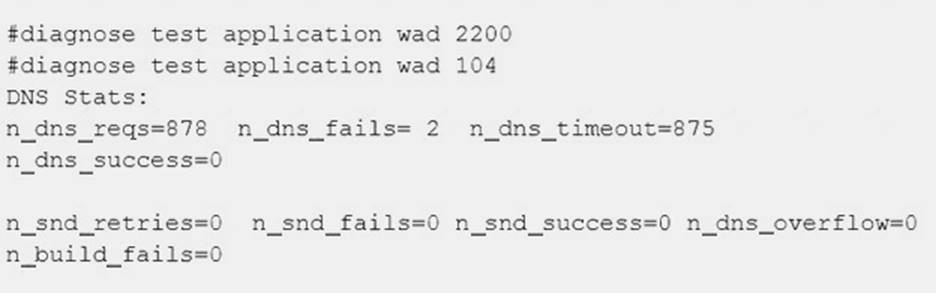
What should the administrator check to fix the problem?
- A. The connectivity between the FortiGate unit and the DNS server.
- B. The connectivity between the client workstations and the DNS server.
- C. That DNS traffic from client workstations isallowed by the explicit web proxy policies.
- D. That DNS service is enabled in the explicit web proxy interface.
Answer: A
NEW QUESTION 13
Which real time debug should an administrator enable to troubleshoot RADIUSauthentication problems?
- A. Diagnose debug application radius -1.
- B. Diagnose debug application fnbamd -1.
- C. Diagnose authd console –log enable.
- D. Diagnose radius console –log enable.
Answer: B
Explanation:
https://kb.fortinet.com/kb/documentLink.do?externalID=FD32838
NEW QUESTION 14
An administrator has configured a FortiGate device with two VDOMs: root and internal. The administrator has also created and inter-VDOM link that connects both VDOMs. The objective is to have each VDOM advertise some routes to the other VDOM via OSPF through the inter-VDOM link. What OSPF configuration settings must match in both VDOMs to have the OSPF adjacency successfully forming? (Choose three.)
- A. Router ID.
- B. OSPF interface area.
- C. OSPF interface cost.
- D. OSPF interface MTU.
- E. Interface subnet mask.
Answer: BDE
NEW QUESTION 15
View the exhibit, which contains a session entry, and then answer the question below.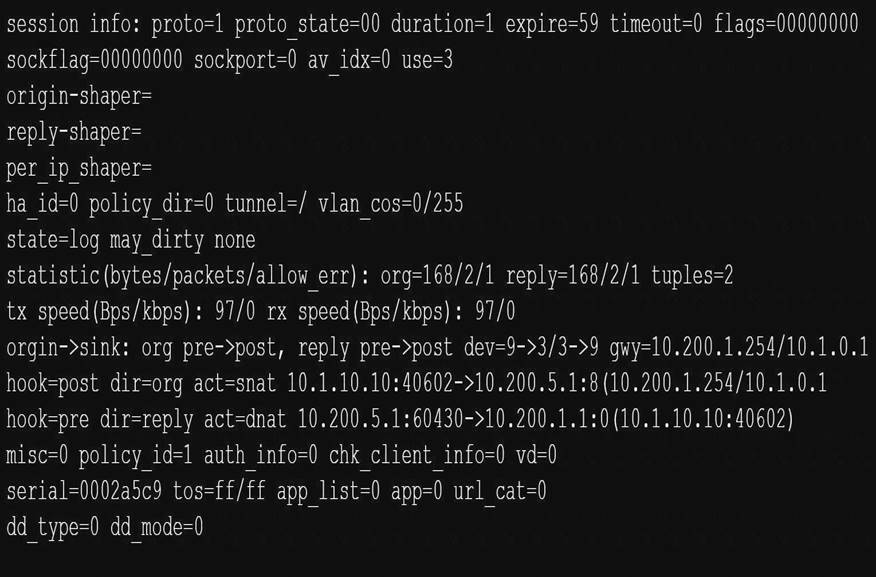
Which statement is correct regarding this session?
- A. It is an ICMP session from 10.1.10.10 to 10.200.1.1.
- B. It isan ICMP session from 10.1.10.10 to 10.200.5.1.
- C. It is a TCP session in ESTABLISHED state from 10.1.10.10 to 10.200.5.1.
- D. It is a TCP session in CLOSE_WAIT state from 10.1.10.10 to 10.200.1.1.
Answer: A
NEW QUESTION 16
View these partial outputs from two routing debug commands:
Which outbound interface will FortiGate use to route web traffic from internal users to the Internet?
- A. Both port1 and port2
- B. port3
- C. port1
- D. port2
Answer: A
NEW QUESTION 17
Examine the following traffic log; then answer the question below.
date-20xx-02-01 time=19:52:01 devname=master device_id="xxxxxxx" log_id=0100020007 type=event subtype=system pri critical vd=root service=kemel status=failure msg="NAT port is exhausted."
What does the log mean?
- A. There is not enough available memory in the system to create a new entry in the NAT port table.
- B. The limit for the maximum number of simultaneous sessions sharing the same NAT port has been reached.
- C. FortiGate does not have any available NAT port for a new connection.
- D. The limit for the maximum number of entries in the NAT port table has been reached.
Answer: B
NEW QUESTION 18
View the exhibit, which contains a screenshot of some phase-1 settings, and then answer the question below.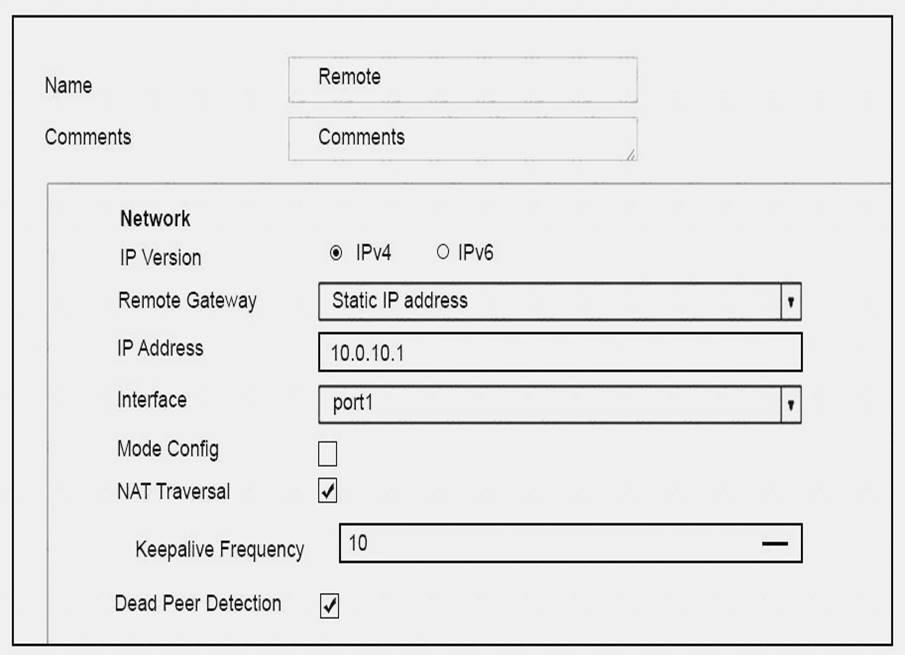
The VPN is up, and DPD packets are being exchanged between both IPsec gateways; however, traffic cannot pass through the tunnel. To diagnose, the administrator enters these CLI commands: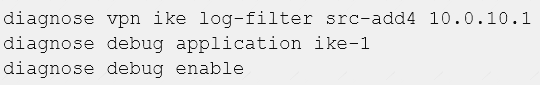
However, the IKE real time debug does not show any output. Why?
- A. The debug output shows phases 1 and 2 negotiations onl
- B. Once the tunnel is up, it does not show any more output.
- C. The log-filter setting was setincorrectl
- D. The VPN’s traffic does not match this filter.
- E. The debug shows only error message
- F. If there is no output, then the tunnel is operating normally.
- G. The debug output shows phase 1 negotiation onl
- H. After that, the administrator must enable the following real time debug: diagnose debug application ipsec -1.
Answer: D
NEW QUESTION 19
A FortiGate is rebooting unexpectedly without any apparent reason. What troubleshooting tools could an administrator use to get more information about the problem? (Choose two.)
- A. Firewall monitor.
- B. Policy monitor.
- C. Logs.
- D. Crashlogs.
Answer: CD
NEW QUESTION 20
What does the dirty flag mean in a FortiGate session?
- A. Traffic has been blocked by the antivirus inspection.
- B. The next packet must be re-evaluated against the firewall policies.
- C. The session must be removed from the former primaryunit after an HA failover.
- D. Traffic has been identified as from an application that is not allowed.
Answer: B
Explanation:
https://kb.fortinet.com/kb/viewContent.do?externalId=FD40119&sliceId=1
NEW QUESTION 21
View the IPS exit log, and then answer the question below.
# diagnose test application ipsmonitor 3 ipsengine exit log”
pid = 93 (cfg), duration = 5605322 (s) at Wed Apr 19 09:57:26 2021 code = 11, reason: manual
What is the status of IPS on this FortiGate?
- A. IPS engine memory consumption has exceeded the model-specific predefined value.
- B. IPS daemon experienced a crash.
- C. There are communication problems between the IPS engine and the management database.
- D. All IPS-related features have been disabled in FortiGate’s configuration.
Answer: D
Explanation:
The command diagnose test application ipsmonitor includes many options that are useful for troubleshooting purposes.Option 3 displays the log entries generated every time an IPS engine process stopped. There are various reasons why these logs are generated:Manual: Because of the configuration, IPS no longer needs to run (that is, all IPS-releated features have been disabled)
NEW QUESTION 22
View the exhibit, which contains the output of a diagnose command, and then answer the question below.
What statements are correctregarding the output? (Choose two.)
- A. This is an expected session created by a session helper.
- B. Traffic in the original direction (coming from the IP address 10.171.122.38) will be routed to the next-hop IP address 10.0.1.10.
- C. Traffic in the originaldirection (coming from the IP address 10.171.122.38) will be routed to the next-hop IP address 10.200.1.1.
- D. This is an expected session created by an application control profile.
Answer: AC
NEW QUESTION 23
View the exhibit, which contains a partial routing table, and then answer the question below.
Assuming all the appropriate firewall policies are configured, which of the following pings will FortiGate route? (Choose two.)
- A. Source IP address 10.1.0.24, Destination IP address 10.72.3.20.
- B. Source IP address 10.72.3.27, Destination IP address 10.1.0.52.
- C. Source IP address 10.72.3.52, Destination IP address 10.1.0.254.
- D. Source IP address 10.73.9.10, Destination IP address 10.72.3.15.
Answer: BC
NEW QUESTION 24
......
P.S. Easily pass NSE7_EFW-6.2 Exam with 91 Q&As 2passeasy Dumps & pdf Version, Welcome to Download the Newest 2passeasy NSE7_EFW-6.2 Dumps: https://www.2passeasy.com/dumps/NSE7_EFW-6.2/ (91 New Questions)
- The Up To Date Guide To NSE7_EFW-6.0 Pdf Exam
- What Top Quality NSE6_FML-6.2 Questions Pool Is
- Most Recent NSE4_FGT-6.2 Lab 2021
- Top Tips Of Up To Date NSE7_EFW-6.4 Testing Material
- The Secret Of Fortinet NSE5_FAZ-6.4 Training
- The Secret Of Fortinet NSE5_FMG-6.0 Exam
- Improved NSE4-5.4 Exam Study Guides With New Update Exam Questions
- Latest Fortinet NSE 5 - FortiClient EMS 7.0 NSE5_FCT-7.0 Pdf
- Validated Fortinet NSE4-5.4 exam question
- What 100% Guarantee NSE7_EFW-6.4 Free Practice Questions Is