156-915.77 Exam Questions - Online Test
156-915.77 Premium VCE File

150 Lectures, 20 Hours
Testking offers free demo for 156-915.77 exam. "Check Point Certified Security Expert Update Blade", also known as 156-915.77 exam, is a CheckPoint Certification. This set of posts, Passing the CheckPoint 156-915.77 exam, will help you answer those questions. The 156-915.77 Questions & Answers covers all the knowledge points of the real exam. 100% real CheckPoint 156-915.77 exams and revised by experts!
Also have 156-915.77 free dumps questions for you:
NEW QUESTION 1
Which command line interface utility allows the administrator to verify the Security Policy name and timestamp currently installed on a firewall module?
- A. cpstat fwd
- B. fw ver
- C. fw stat
- D. fw ctl pstat
Answer: C
NEW QUESTION 2
Configure the new interface via sysconfig from the "non-member" Gateway.
Solution:
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 3
If Jack was concerned about the number of log entries he would receive in the SmartReporter system, which policy would he need to modify?
- A. Log Sequence Policy
- B. Report Policy
- C. Log Consolidator Policy
- D. Consolidation Policy
Answer: D
NEW QUESTION 4
MultiCorp has bought company OmniCorp and now has two active AD domains. How would you deploy Identity Awareness in this environment?
- A. You must run an ADquery for every domain.
- B. Identity Awareness can only manage one AD domain.
- C. Only one ADquery is necessary to ask for all domains.
- D. Only Captive Portal can be used.
Answer: A
NEW QUESTION 5
You are troubleshooting a HTTP connection problem. You've started fw monitor -o http.pcap. When you open http.pcap with Wireshark there is only one line. What is the most likely reason?
- A. fw monitor was restricted to the wrong interface.
- B. Like SmartView Tracker only the first packet of a connection will be captured by fw monitor.
- C. By default only SYN pakets are captured.
- D. Acceleration was turned on and therefore fw monitor sees only SYN.
Answer: D
NEW QUESTION 6
MultiCorp is running Smartcenter R71 on an IPSO platform and wants to upgrade to a new Appliance with R77. Which migration tool is recommended?
- A. Download Migration Tool R77 for IPSO and Splat/Linux from Check Point website.
- B. Use already installed Migration Tool.
- C. Use Migration Tool from CD/ISO
- D. Fetch Migration Tool R71 for IPSO and Migration Tool R77 for Splat/Linux from CheckPoint website
Answer: A
NEW QUESTION 7
CORRECT TEXT
In a zero downtime scenario, which command do you run manually after all cluster members are upgraded?
Solution:
cphaconf set_ccp multicast
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 8
Peter is your new Security Administrator. On his first working day, he is very nervous and enters the wrong password three times. His account is locked. What can be done to unlock Peter’s account? Give the BEST answer.
- A. You can unlock Peter’s account by using the command fwm lock_admin -u Peter on the Security Management Server.
- B. You can unlock Peter’s account by using the command fwm unlock_admin -u Peter on the Security Management Server
- C. It is not possible to unlock Peter’s accoun
- D. You have to install the firewall once again or abstain from Peter’s help.
- E. You can unlock Peter’s account by using the command fwm unlock_admin -u Peter on the Security Gateway.
Answer: A
NEW QUESTION 9
Review the Rule Base displayed.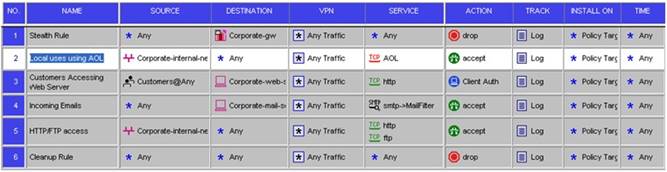
For which rules will the connection templates be generated in SecureXL?
- A. Rules 2 and 5
- B. Rules 2 through 5
- C. Rule 2 only
- D. All rules except Rule 3
Answer: D
NEW QUESTION 10
CORRECT TEXT
Type the command and syntax to configure the Cluster Control Protocol (CCP) to use Broadcast.
Solution:
cphaconf set_ccp broadcast
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 11
Select the correct statement about Secure Internal Communications (SIC) Certificates. SIC Certificates:
- A. Are used for securing internal network communications between the SmartDashboard and the Security Management Server.
- B. For R75 Security Gateways are created during the Security Management Server installation.
- C. Decrease network security by securing administrative communication among the Security Management Servers and the Security Gateway.
- D. Uniquely identify Check Point enabled machines; they have the same function as VPN Certificates.
Answer: D
NEW QUESTION 12
Which operating systems are supported by a Check Point Security Gateway on an open server? Select MOST complete list.
- A. Sun Solaris, Red Hat Enterprise Linux, Check Point SecurePlatform, IPSO, Microsoft Windows
- B. Check Point GAiA and SecurePlatform, and Microsoft Windows
- C. Check Point GAiA, Microsoft Windows, Red Hat Enterprise Linux, Sun Solaris, IPSO
- D. Check Point GAiA and SecurePlatform, IPSO, Sun Solaris, Microsoft Windows
Answer: B
NEW QUESTION 13
Which Check Point tool allows you to open a debug file and see the VPN packet exchange details.
- A. PacketDebug.exe
- B. VPNDebugger.exe
- C. IkeView.exe
- D. IPSECDebug.exe
Answer: C
NEW QUESTION 14
CORRECT TEXT
To stop acceleration on a GAiA Security Gateway, enter command:
Solution:
fwaccel off
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 15
You have created a Rule Base for firewall, websydney. Now you are going to create a new policy package with security and address translation rules for a second Gateway.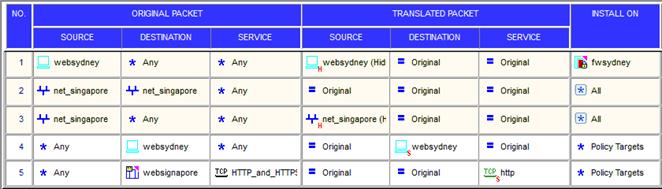
What is TRUE about the new package’s NAT rules?
- A. Rules 1, 2, 3 will appear in the new package.
- B. Only rule 1 will appear in the new package.
- C. NAT rules will be empty in the new package.
- D. Rules 4 and 5 will appear in the new package.
Answer: A
NEW QUESTION 16
Because of pre-existing design constraints, you set up manual NAT rules for your HTTP server. However, your FTP server and SMTP server are both using automatic NAT rules. All traffic from your FTP and SMTP servers are passing through the Security Gateway without a problem, but traffic from the Web server is dropped on rule 0 because of anti- spoofing settings. What is causing this?
- A. Manual NAT rules are not configured correctly.
- B. Allow bi-directional NAT is not checked in Global Properties.
- C. Routing is not configured correctly.
- D. Translate destination on client side is not checked in Global Properties under Manual NAT Rules.
Answer: D
NEW QUESTION 17
......
Recommend!! Get the Full 156-915.77 dumps in VCE and PDF From Dumpscollection.com, Welcome to Download: https://www.dumpscollection.net/dumps/156-915.77/ (New 203 Q&As Version)
- Improved Check Point Certified Security Expert Update Blade 156-915.77 Testing Material
- All About Top Quality 156-915.77 Vce
- Abreast Of The Times 156-585 Test For Check Point Certified Troubleshooting Expert Certification
- Avant-garde 156-915.77 Testing Bible For Check Point Certified Security Expert Update Blade Certification
- How Many Questions Of 156-585 Sample Question
- What Validated 156-915.77 Exam Dumps Is